Independent public record · Project Sun Rock / Por Derecho · not a CajaSiete website · no affiliation or appearance of an official CajaSiete communication
PROJECT SUN ROCK · POR DERECHO
CAJASIETE · COMMUNICATION 6 · INSTITUTIONAL REVIEW

A directly affected party. A reporting person since 2021. A finite question of records and traceability.

Gil Marer / Aweswell Limited / Project Sun Rock · Por Derecho. We appear as a party directly and indirectly affected by the facts and their economic and legal consequences and, separately, in the stated capacity of a reporting person / whistleblower who since 2021 has communicated facts, documents and allegations considered grounded and in the public interest to authorities, regulators, professional bodies and other competent recipients.

The question now put to CajaSiete is limited: what the institution received, what it verified, who decided, what conflict and independence controls it applied, and what institutional trace remains.

90-second institutional read

CAPACITY 1 · AFFECTED PARTY

Direct interest, kept separate

Aweswell Limited and the Sun Rock perimeter allege economic, corporate, proprietary and procedural harm connected with the former Sun Park and its later evolution. That affected-party capacity is distinct from the reporting-person capacity.

CAPACITY 2 · REPORTING PERSON / WHISTLEBLOWER

Documented reporting continuity since 2021

The record preserves formal communications from January 2021 concerning Sun Park / RIC Private Equity. That reporting continuity predates Spain's Law 2/2023 and continues under later frameworks where applicable; this page does not present universal protected status as already determined by an authority.

We are not asking CajaSiete to adjudicate the whole Sun Park dispute. We are asking CajaSiete to account for its own records, its own decisions, its own conflict controls, its own exposure and its own handling of information received from an affected party who has also been reporting public-interest allegations to competent bodies since 2021.
Documented10 Dec 2025 → 9/28 Apr 2026 → 5/18 Sep 2026

Independence/conflict assurances, receipt, inadmission, CNMV supplement and reaffirmation.

Not yet explained externallyDecision ownership · conflict check · audit trail

The external explanation gap does not prove the absence of internal controls.

Not assertedMortgage = crime · Orion = coordination · silence = illegality

Association, financing, receipt or proximity do not replace actor-specific proof.

Reporting-person continuity: from January 2021

13 JAN 2021 · CNMV + AEAT

First controlled regulatory checkpoint

The CNMV communication was registered as 2021002141. An AEAT telematic registry record from the same date documents a tax complaint concerning possible investor fraud through RIC materialisation. Those records prove intake/receipt, not fraud or a merits finding.

Open the 2021 documentary node →

2021 → 2026

The subject expanded with later documents

The 2021 notice concerned RICPE/Sun Park, investor representations, title/control and RIC. Later evidence separately identified regional-incentives file GC/836/P06 and a FEDER/ERDF layer. Those later records are not backdated into what any recipient knew in 2021.

RICPE / HNT / GC836 → · EU funds / traceability →

Five finite questions for an institutional response

1 · DECISIONWho was competent?

The function that classified, proposed and adopted the April inadmission and September review/reaffirmation.

2 · CONFLICTSWhat check was performed?

Which function tested independence/conflicts and whether recusal, reassignment or a second review was considered.

3 · TRACEABILITYWhat trace remains?

Receipt, access, classification, assessment, decision, transfer, retention, anonymisation or deletion.

4 · DISTRIBUTIONWhere did the escalation go?

Which Management, Board, Audit/Risk, Compliance, AML, Legal and Internal Audit functions received it.

5 · RESPONSEWho owns it now?

Which function coordinates one attributable response compatible with confidentiality and third-party secrecy.

Precision on the Audit & Risk Commission. CajaSiete's published regulation does not by itself establish that the Commission had to decide the initial admissibility of Communication 6. Its Ethical Channel provision concerns valid reports that have passed through investigation. If the communication was excluded before that stage, the proper question is narrower: which function held threshold authority, under what procedure, and what governance or independent-review mechanism oversees that decision. CajaSiete's published regulation →
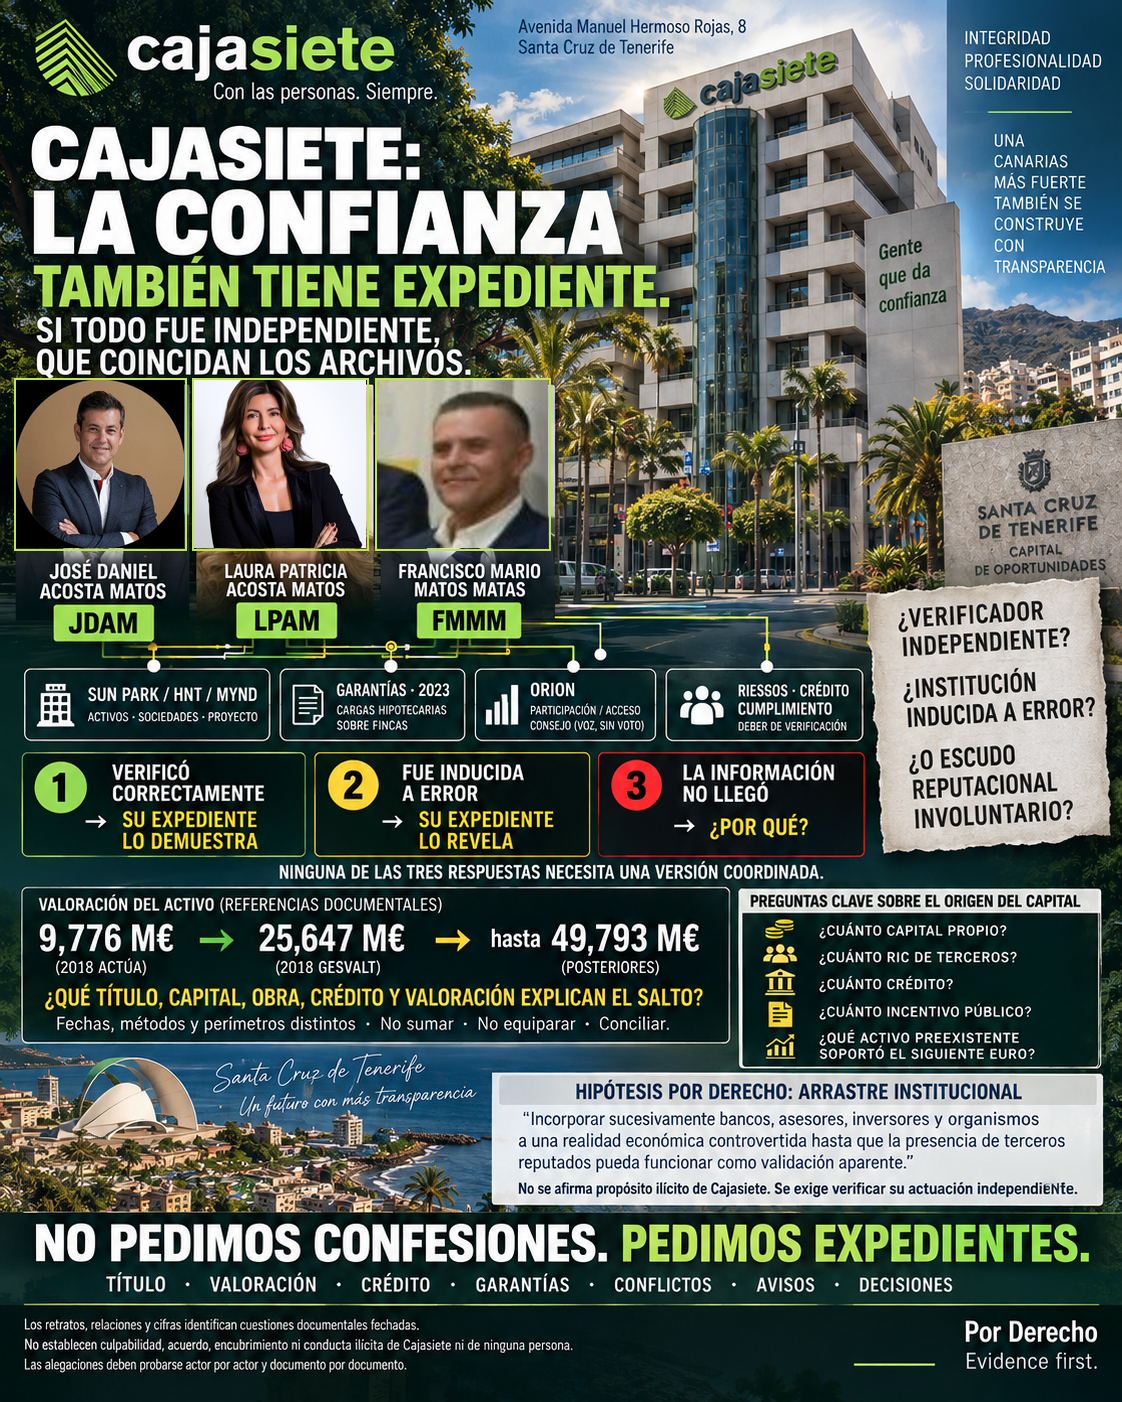
Secondary explanatory visual · editorial composition, not a CajaSiete document
Independent editorial composition about records and verification; not CajaSiete corporate material

Independent editorial composition. It is not documentary photography of an event or CajaSiete corporate material. Portraits and connecting lines are orientation aids and do not establish coordination, common knowledge or unlawful conduct. Open the independent-verification page →

INDEPENDENT CONTROLS SHOULD LEAVE AN INSTITUTIONAL TRACE.

If controls worked, the record can demonstrate it. If information was incomplete, the record can reveal it. If routing failed, the audit trail can explain it. If no further action is warranted, the competent function can identify the basis.

1. CajaSiete relationships and actions documented in this record

DOCUMENTED · SECURITY

3 October 2023 · Sun Park / HNT

The project's controlled documentary register identifies CajaSiete mortgage charges over several former Sun Park properties later associated with Hotel New Trend / MYND Yaiza.

Still open: borrower, cash principal, instrument, valuation, purpose, approving body, drawdowns, additional collateral and full perimeter.

DOCUMENTED · ORION

Investment and corporate access

Public Orion documents record a CajaSiete shareholding at dated points and a historical right to attend the board with voice but without vote. The Acosta Matos perimeter also appears in Orion's structure.

Equity, lending and information access must be analysed separately; none alone proves unlawful coordination.

DOCUMENTED · CANARY FINANCE

Public debt / RIC

Canary Government material preserved in the repository lists CajaSiete among financial institutions in financing/debt operations across several years, including RIC routes. This broadens the institutional map but does not prove those public-finance operations funded Sun Park.

DOCUMENTED · ETHICS CHANNEL

Substantive decisions without a named personal signatory

The bank gave independence/conflict assurances in December 2025; Communication 6 was received in April 2026, rejected on 28 April with announced destruction, and that decision was reaffirmed on 18 September after further official CNMV material.

The latest response still does not identify the decision owner or explain the requested conflict and traceability controls.

2. Ethics Channel accountability chronology

Prior request for independence and conflict assurances

Gil Marer asked for confirmation of case opening, independence, absence of conflict, confidentiality and protection before providing the structured evidence. Native private source retained; public-safe derivative only.

CajaSiete promises independence, traceability and recusal/reassignment

“Gestor del Canal Cajasiete” directed the informant to the Internal Information System and said the Criminal Compliance Body/channel managers acted independently; if a potential conflict were identified, recusal/reassignment measures would be used.

Communication 6 received

The Ethics Channel platform confirmed receipt and assigned an identifier. No access credential is published here.

Inadmission + announced destruction

The platform stated inadmission reasons including public information/rumour, a possible personal conflict outside the organisation, scope exclusion and inability to investigate; it said the information would be destroyed under applicable rules. The notice does not prove actual destruction or its scope.

Official CNMV material and traceability questions added

Two official CNMV documents were supplied and CajaSiete was expressly asked to identify the independent reviewing function, the incorporation reference, conflict analysis, and lawful preservation/anonymisation/deletion position.

Reaffirmation: “no change” to April decision

“Gestor del Canal Cajasiete” said the additional documentation had been incorporated and did not alter the April outcome, and that the material remained registered with confidentiality/restricted access. It did not identify the decision owner, answer the requested conflict-control question, or describe the decision/preservation audit trail.

3. The institutional-control question is finite and testable

No presumption of guilt is required. The test is whether CajaSiete's own financial/corporate exposure required a different independent review; whether inadmission prevented examination of facts relevant to the bank's own relationships; who took that decision; what each function knew at each date; and what the bank did after notice.
TestQuestion to be answered from records
KnowledgeWhat title, litigation, Insolvency 36/2012, actor, valuation and operating information did CajaSiete have when each facility/security decision was made?
ConflictDid HNT/CAM finance, Orion equity/access or other relationships require recusal, reassignment or a distinct independent second line when Communication 6 arrived?
DecisionWho classified, proposed and approved the 28 April inadmission and 18 September review/reaffirmation?
Document baseWhat was actually reviewed, and what individualised reasoning supported each inadmission ground?
PreservationWhat was retained, transferred, anonymised or deleted; when; by whom; on what basis; and what audit metadata remain?
Post-notice conductAfter notice, what risk, compliance, related-party, credit, valuation or governance checks were performed and with what result?
Benefit/lossWhat facilities, security, interest, fees, equity or economic exposure are actually linked by date and instrument? Association is not unlawful benefit.

3A. One chronology, different legal-control lanes

Control rule: RIC, RICPE/CNMV, Regional Incentives and ERDF are not the same funding source or legal regime. Their coexistence does not establish double funding, fraud or money laundering. The narrower CajaSiete question is what the bank knew about each layer when it took exposure, accepted security or received later alerts, and how that information was reconciled across credit, risk, compliance, AML and governance.
LaneExisting fact/controlBounded CajaSiete questionPublic reference
RIC / taxRIC is a tax incentive governed by materialisation, financing and aid-accumulation rules; associated aid/incentives must be reported under the applicable regime.Where material to the transaction, did the credit/KYC file identify the origin and structure of RIC capital or other aid/incentives funding the same project, and reconcile them with debt, own funds and security?Law 19/1994 · RD 1758/2007
RICPE / CNMVThe public record documents Sun Park/MYND as a RICPE project and CNMV activity; the 22 January 2026 response defines documents not found among material obtained in those supervisory actions.Were CajaSiete's own Orion relationships and later HNT/MYND security layer identified in the conflict/independence analysis when Communication 6 and the new CNMV material were reviewed?CNMV/RICPE · RICPE/Sun Park
Regional IncentivesPublic file GC/836/P06 identifies investment, grant and employment figures; the complete file, payments, eligible costs, other aid and controls remain reconciliation targets.If the grant was material to project finance, works, valuation, covenants or repayment, what information entered underwriting and what check was made on other finance/aid sources?GC/836/P06 · Directorate-General for European Funds
ERDFThe public project record identifies an ERDF layer, while the exact programme, operation, percentage, certified expenditure, payments, audits and corrections remain open.Did the bank file record the existence and scope of ERDF support if material to finance, works or valuation? If not, was this revisited after the alerts?ERDF / SNCA · RIC–incentives–ERDF chain
Prudential governanceLaw 10/2014 requires clear responsibility lines, risk identification/control/communication, adequate internal controls and conflict prevention; the Board is accountable for the system's effectiveness.Which body owns this review, which control functions acted, and what remediation follows if a routing, conflict or control weakness is identified?Law 10/2014, art. 29 · Banco de España
AMLLaw 10/2010 requires a written special examination of facts or transactions that are complex, unusual or present indicators of simulation or fraud where the statutory threshold is met.Did AML assess whether the known facts required a special examination under its procedures? No confirmation of any SEPBLAC report is requested or should be disclosed, because tipping-off is prohibited.Law 10/2010, arts. 17, 18 and 24

3B. Four lawful exits: every one needs a record

EXIT 1

The controls worked

CajaSiete can document what it verified, who verified it, what conflict was ruled out, which body decided and why. That outcome should be reflected faithfully in the public record.

EXIT 2

It received incomplete or incorrect information

Identify what was missing or wrong, when it was detected, its impact and what correction/escalation follows. That does not automatically make the bank responsible for information it received.

EXIT 3

Routing or control failed

Identify why information did not reach the proper function, preserve the trail and correct the process. A routing failure does not by itself establish intent.

EXIT 4

No further action is required

CajaSiete can take that position, but should identify the competent function, the basis applied and the conflict control supporting it. A generic signature does not replace that explanation.

Control design, documentation and correction. No function is asked to accuse another. Each function records only what it did, what it received, what conflict it assessed and what it escalated. Compatible answers reinforce each other; incompatible answers become objectively testable audit or supervisory questions.

3C. Control questions by function: one issue, one responsible function

FunctionControl questionDocumentable output
Governing Board / ChairHas the matter been received and have clear responsibility lines, independence and conflict prevention been ensured?Date of knowledge, assigned body, governance action and follow-up.
Audit & Risk CommissionHas it reviewed or assumed oversight of the Ethics Channel handling and connected exposure/risk?Confirmation of review, instructing function and status; confidential minutes are not requested.
Director GeneralHas Compliance, Risk, AML, Internal Audit and Legal received the parts within their mandates?Routing map and institutional owner.
Regulatory ComplianceWhat compliance/conflict risk was identified and how was independence preserved?Conflict analysis, recusal/reassignment and bounded conclusion.
RiskWhat title, valuation, borrower, security, material finance/support sources and litigation were recorded when exposure was approved or monitored?Confirmation of internal reconciliation without disclosing third-party bank secrecy.
Global Risk ControlDid the second line validate consistency across credit, valuation, security, related parties and new adverse information?Independent test and any remediation.
AMLWas it assessed whether known facts triggered the internal special-examination duty?Confirmation that the relevant procedure was applied, without disclosing protected SEPBLAC communications.
Internal AuditCan it reconstruct who accessed, classified, decided, retained, anonymised or deleted?Audit trail and design/effectiveness test.
LegalWhat procedure, legal basis and confidentiality limits were applied?Procedure version, legal basis and lawful preservation.
Institutional RelationsWas the notice distributed intact to the competent functions?Delivery/routing confirmation; no merits decision is attributed to this function.

4. Law 2/2023 requires a System Officer and an identifiable management architecture

LAW 2/2023 · ART. 8

System Officer

The governing body appoints a natural person responsible for the Internal Information System; if a collegiate body is used, one member must be delegated management and investigation powers. Appointments/removals are notified to the competent authority.

Consolidated BOE text

LAW 2/2023 · ART. 26

Information register

Obliged entities must keep a confidential register of reports and resulting internal investigations. It is not public; the public question here is decision ownership and traceability, not indiscriminate access to protected data.

LAW 2/2023 · ART. 32

Data, access and retention

The statute limits access and provides for deletion/anonymisation under conditions. Deleting personal/report data and erasing responsibility traceability are not the same proposition.

CAJASIETE · PUBLIC STATEMENT

The bank says a System Officer exists

CajaSiete states publicly that it has appointed a Responsable del Sistema Interno de Información and that its channel managers include the Technical Criminal Compliance Unit.

CajaSiete Ethics Channel · Criminal compliance

5. Escalation to identifiable governance and control functions

CajaSiete's own published composition allows the issue to be directed to identifiable governance and control functions without assuming that any listed person participated in the historic events or channel decision.

Internal competence published by the bank itself. The Audit & Risk Commission regulation assigns the Commission regulatory-compliance oversight, investigation of irregular conduct and third-party complaints and, expressly, responsibility for the Ethics Channel and decisions on files arising from valid reports that have undergone investigation. It provides for technical support in the investigation phase from the Ethics & Conduct Committee and Internal Audit. Communication 6 can therefore be escalated to an identifiable, auditable governance function; a generic channel signature does not exhaust that accountability architecture.

Audit & Risk Commission regulation · published last review 24/03/2025

Manuel del Castillo González
Chair · Governing Board
María Dolores Pérez Martínez
Chair · Audit & Risk Commission
Samuel Cruz Palenzuela
Secretary · Audit & Risk Commission
Belinda Anta Jiménez
Member · Audit & Risk Commission
Luis Alberto Díaz Dorta
Director General
María Coromoto Trujillo Pérez
Director of Regulatory Compliance
Sara González Febles
Director of Internal Audit
Juan Miguel López Luis
Director of Risk
Miguel Ángel Rivero Romero
Director of Global Risk Control
Juan Alberto González Dorta
Director of Legal
José Manuel Garrido García
Director of Institutional Relations

CajaSiete published composition · December 2025

6. Institutional review requested from the Board, Audit & Risk, Compliance and Internal Audit

  1. Governing Board: confirm receipt and assign an institutional owner for this review, insulated from relevant commercial exposure.
  2. Audit & Risk Commission: open a governance review of Communication 6 and the 18 September response, recording conclusions and remedial measures in minutes.
  3. System Officer / Compliance: confirm whether the RSII is an individual or collegiate body; confirm appointment notification to the competent authority; identify at least the function/person with decision responsibility or state the specific legal basis for withholding identity.
  4. Conflicts: document what conflict check occurred before inadmission and whether recusal/reassignment was considered under the 10 December 2025 assurance.
  5. Internal Audit: verify the audit trail for receipt, access, classification, assessment, decision, communications, retention, anonymisation and any deletion.
  6. Risk: reconstruct relevant CajaSiete exposures concerning Sun Park/HNT/MYND, Orion and related perimeters by instrument, date, borrower, collateral, valuation, approver, related parties, drawdown and repayment.
  7. Legal: identify the internal procedure/version applied to Communication 6 and the basis for each inadmission ground and any destruction/anonymisation.
  8. Preservation: lawfully retain metadata, logs, minutes, conflict checks, reassignments, decisions and cross-references; this does not ask the bank to retain data whose deletion is legally mandatory.
  9. Response: issue one attributable, documented response distinguishing facts, confidentiality limits, decisions and open points.

7. Reserved external routes, by competence

Independent Whistleblower Protection Authority

For Internal Information System, System Officer and Law 2/2023 guarantee issues, subject to explicit competence determination where required.

AIPI

Banco de España

CajaSiete is listed as credit institution ES3076. The prudential issue would be governance, internal control, compliance independence, conflicts and traceability—not transforming a private dispute into a supervisory conclusion.

BdE register

ECB / SSM

Reserved where facts engage EU prudential rules or warrant additional supervisory routing. This page does not assert material jurisdiction over every allegation.

Criminal / insolvency authorities

Any criminal, insolvency or recovery relevance depends on individualised acts, knowledge, duty, causation, benefit/loss and admissible evidence. This page is not a complaint or adjudication.

8. Evidence boundaries and correction right

This page does not say: CajaSiete funded the original 2018 acquisition; a mortgage charge equals cash drawn; every Board member knew the report; announced destruction actually occurred; or equity, lending or institutional proximity by itself proves intent or crime.

It does document this question: financial/corporate exposure, receipt of an alert touching that same environment, and later substantive decisions communicated without externally identifying the decision owner or explaining the requested conflict and traceability controls. That calls for a governance response, not another anonymous response.

Control sources and links